Fraud Program

Find What Your Fraud Program Isn't Built to Catch, Before a Loss Event Does.

A diagnostic on your fraud program for fintechs and financial institutions: which fraud schemes your controls cover, where the gaps are, and what to fix first. Re-run it after every loss event, control change, or new typology.

Complete your initial diagnostic assessment in 2-3 hours. Self-paced — pause and resume anytime. No preparation required.

Tailored to your institution type, size, and operating geography — not a generic checklist.

FATF 40 • FTC Red Flags • GDPR • PCI DSS

Built by practitioners

Enterprise risk and fraud professionals, not just developers

Secure by design

No names. No free-text. Nothing sensitive.

No AI agents

Auditable analysis. No autonomous actions. No black-box results.

When institutions come to us

Internal audit flagged gaps.

The audit report named specific fraud controls that are missing or untested. You need a program-level view — with prioritized remediations — before the next board committee meeting.

An examination is coming up.

Safety and soundness examiners review fraud controls alongside credit and operational risk. A well-documented fraud risk program is expected — not optional. VeloRisk gives you one in hours, not months.

A fraud event happened — or nearly did.

A payment fraud attempt, an account takeover, or an internal theft incident raised questions about whether your controls are adequate. The answer needs to be documented, and the gaps need to be closed.

Start Your Diagnostic — from $7,499/yr

30-day satisfaction guarantee.

See Your Program in Action

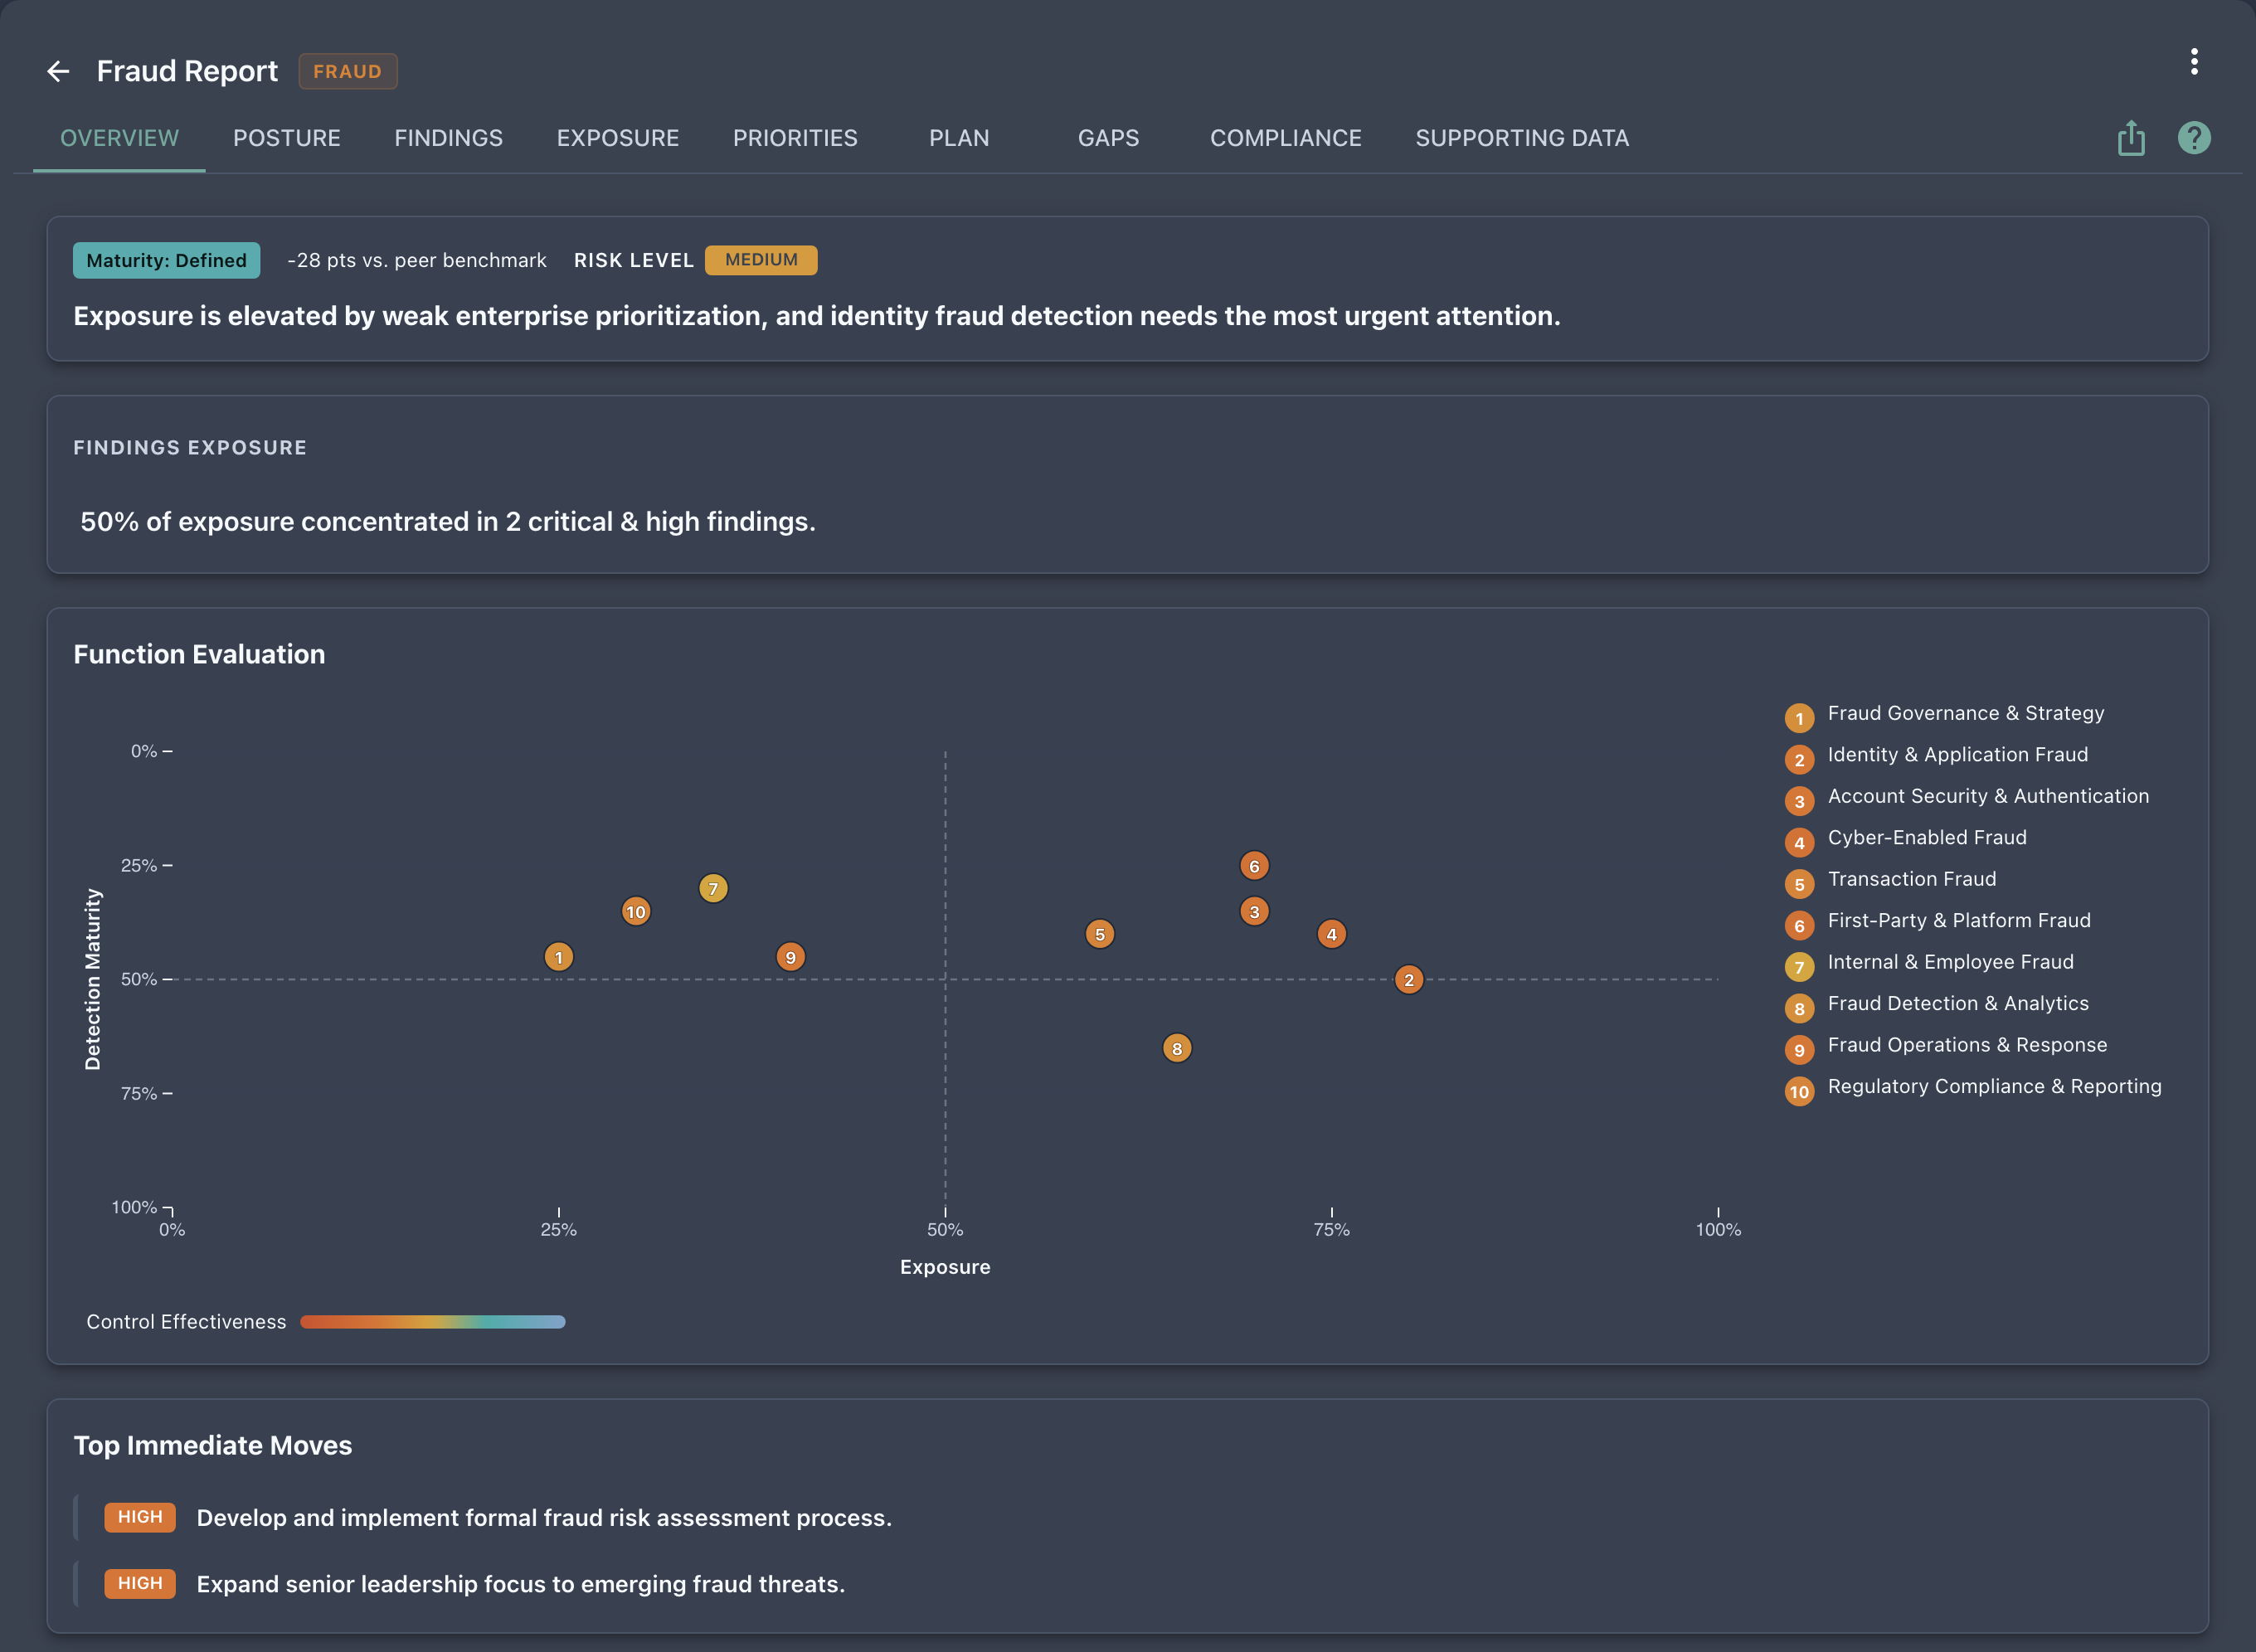
This is what the diagnostic hands you: fraud risk posture across your domains, findings by severity and function, and exposure against maturity for each function. Sample data.
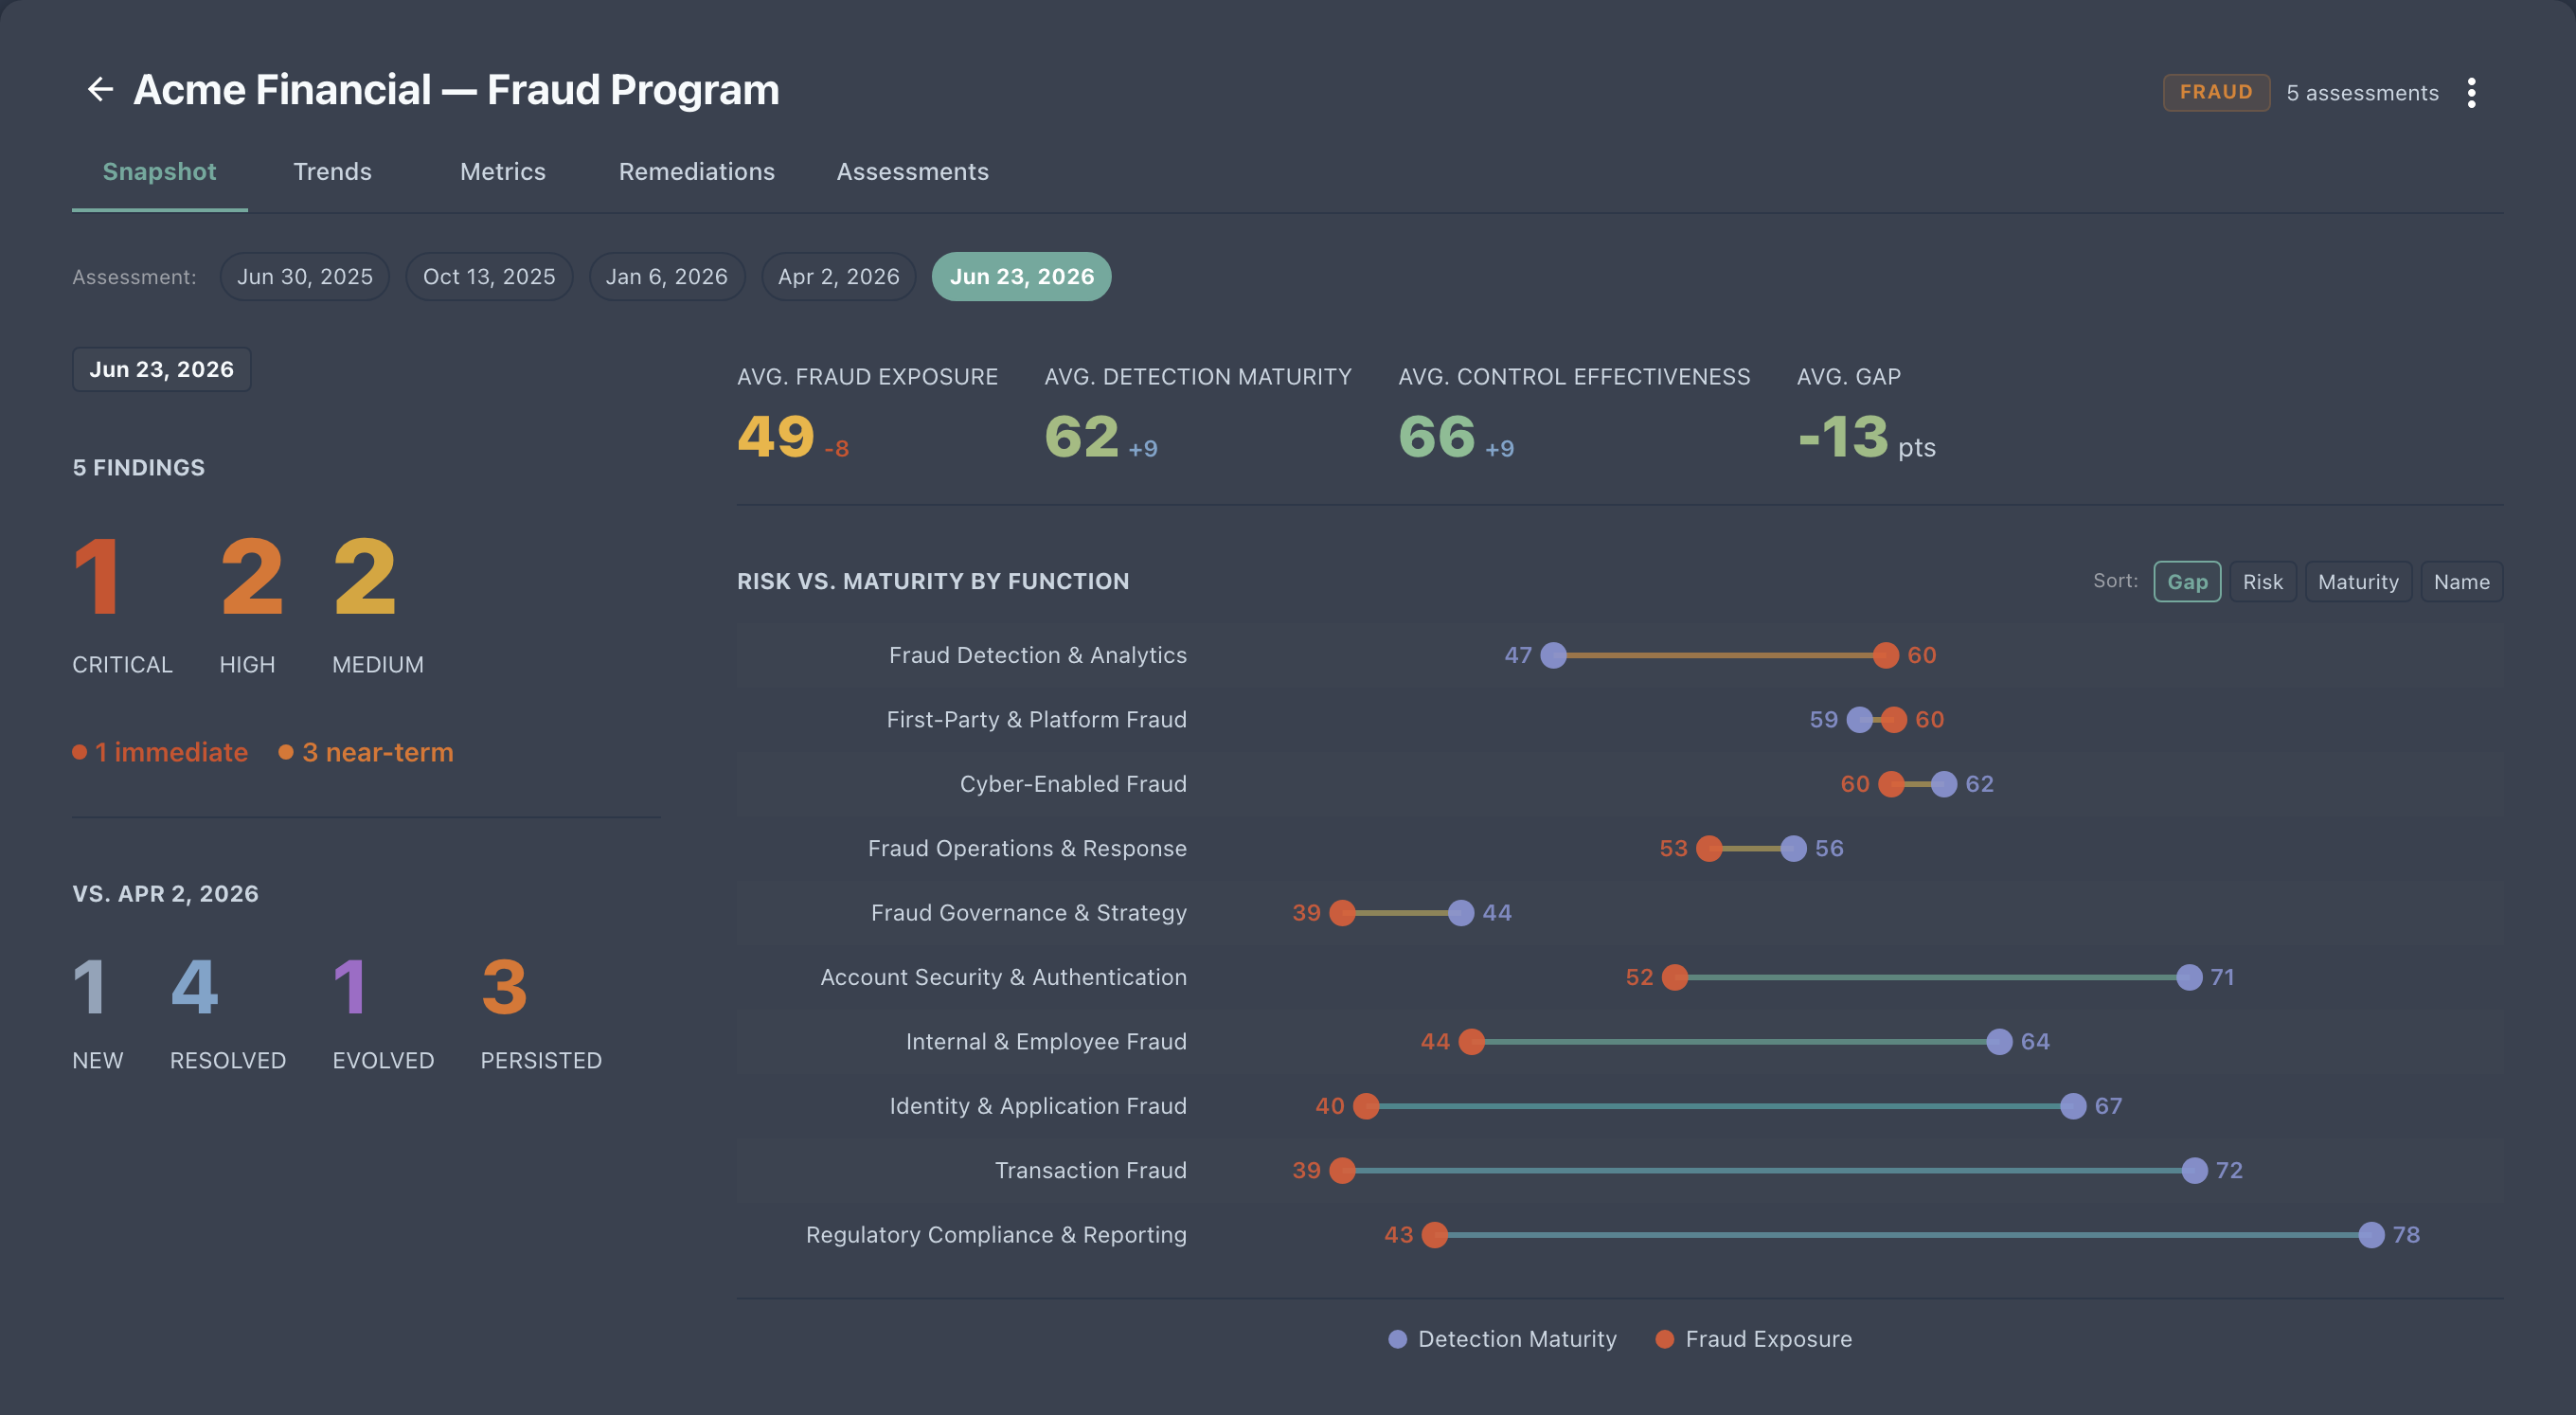
Fraud Program Dashboard — risk posture overview across fraud domains

Program Dashboard — risk posture at a glance
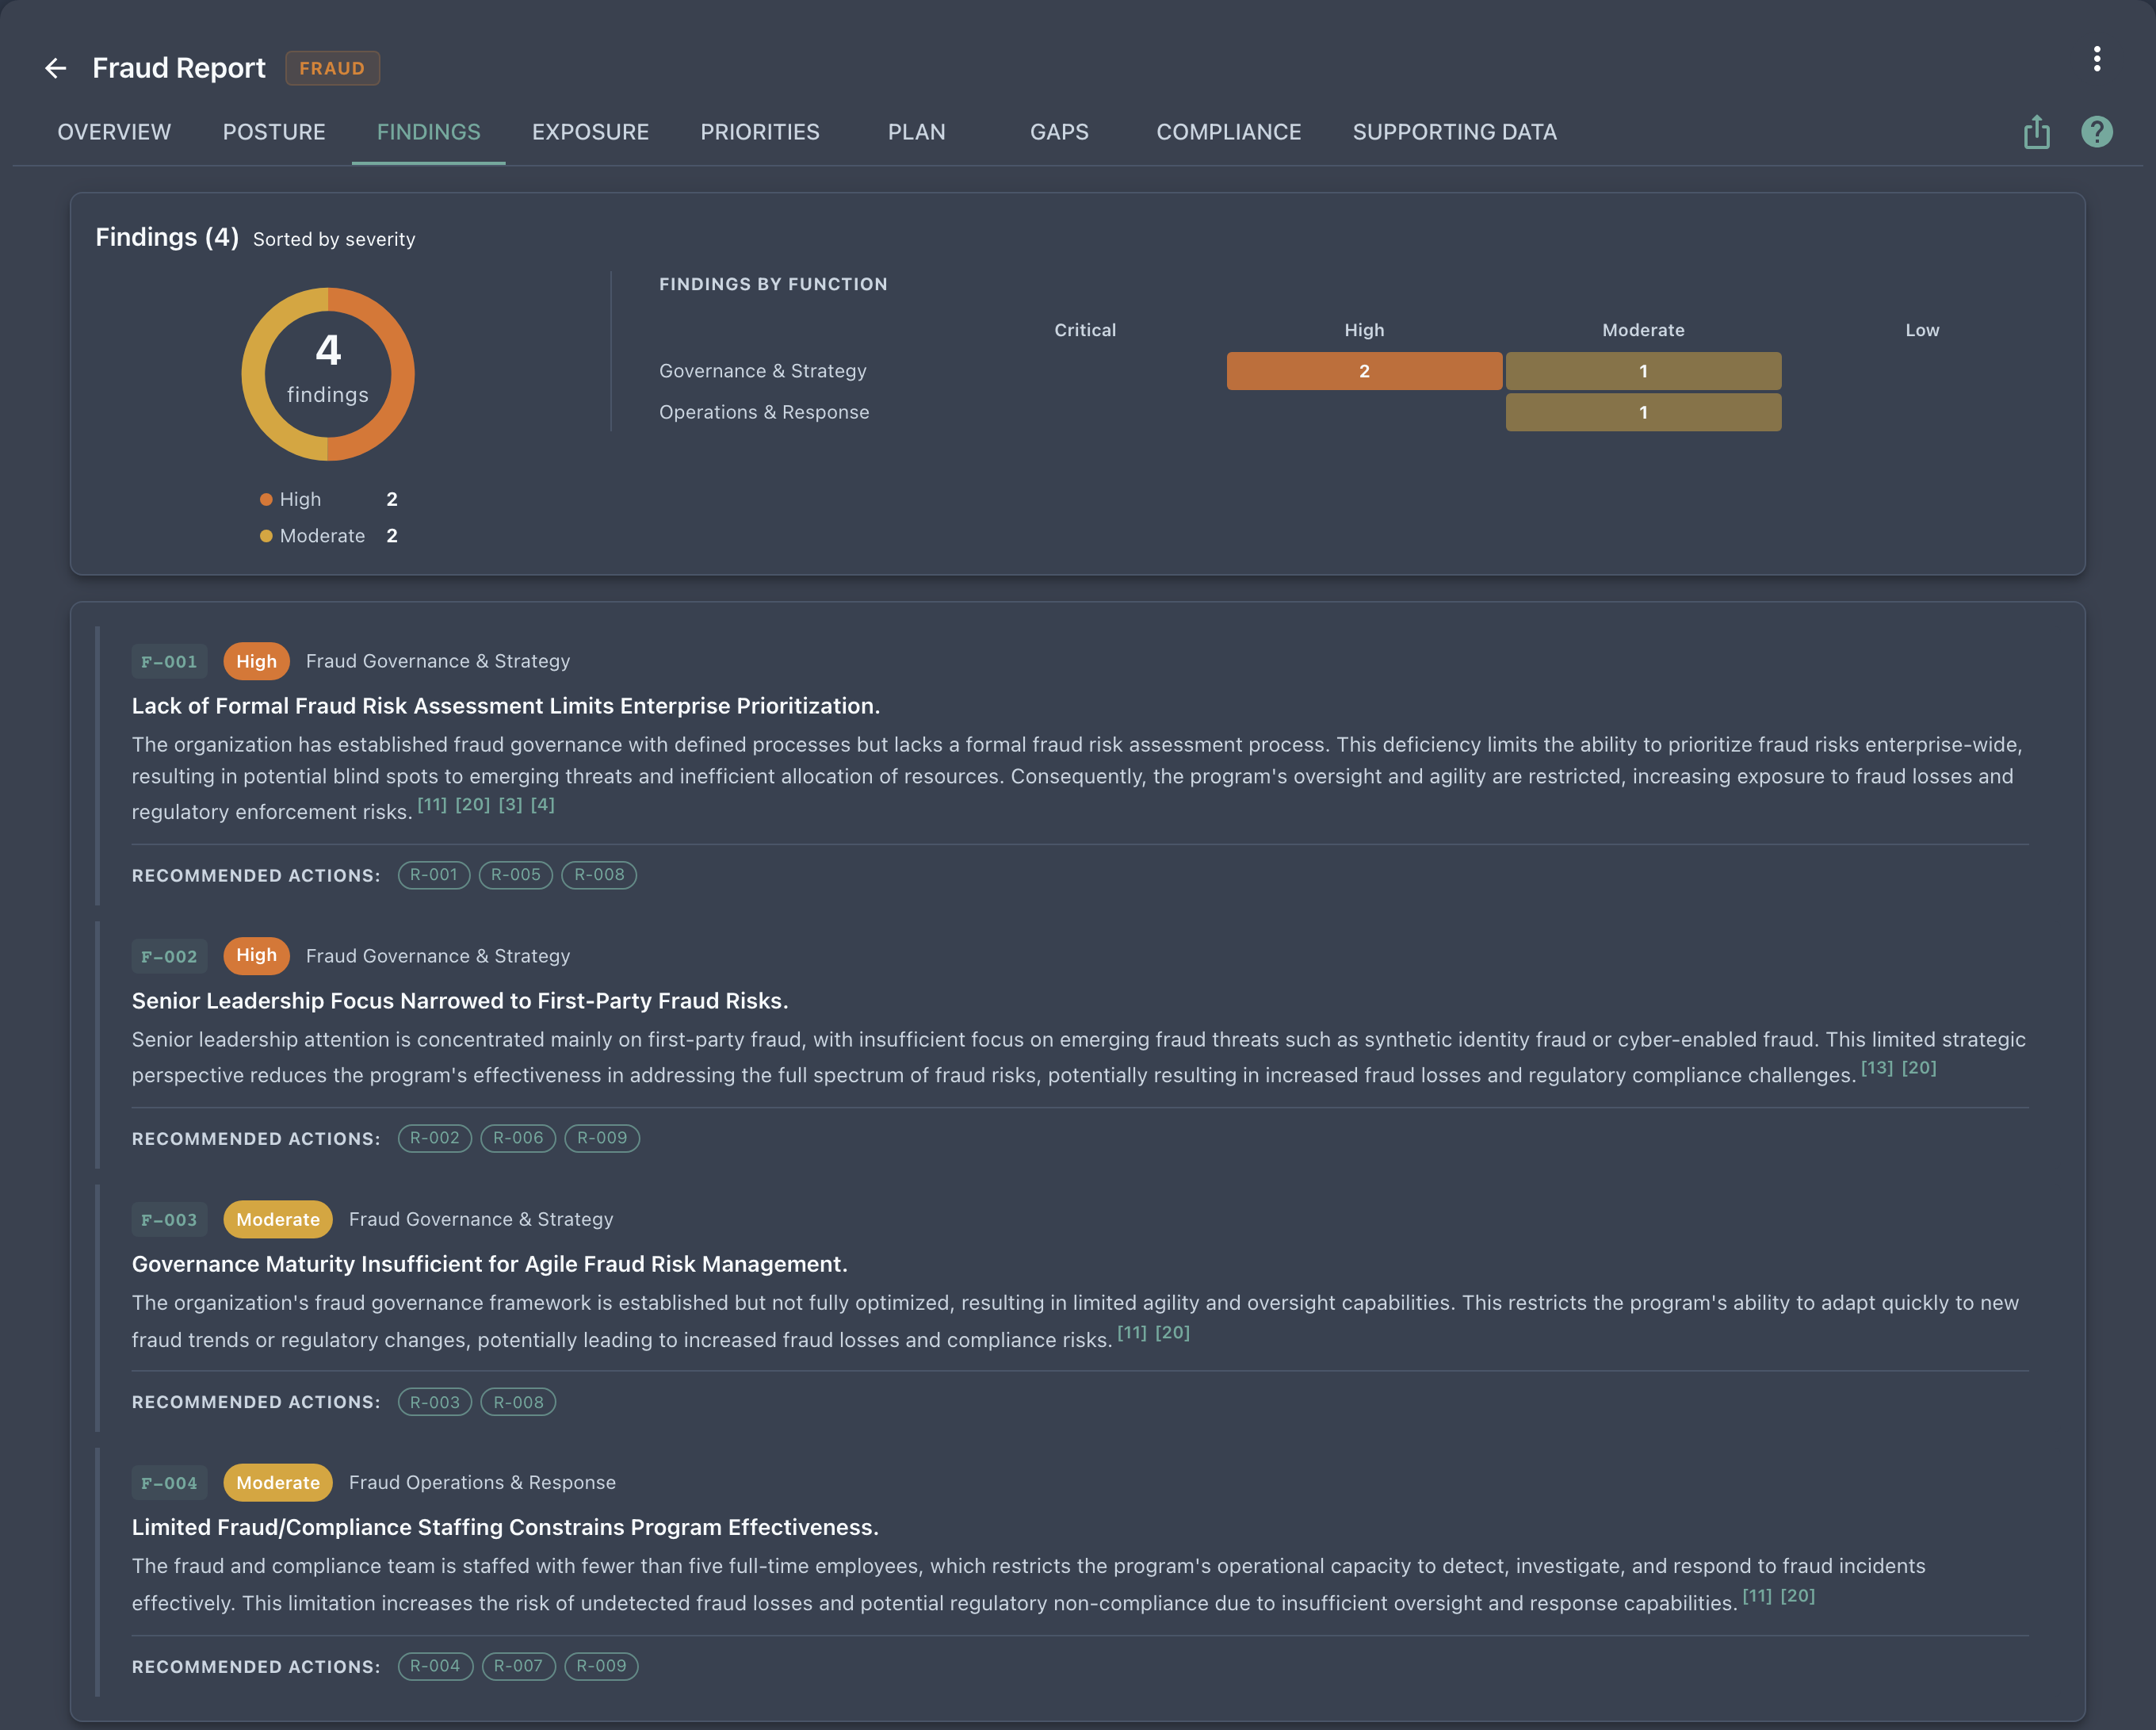
Fraud assessment report — findings by severity and function with recommended actions
Assessment report — findings by severity and function

Fraud assessment report — maturity verdict, exposure concentration and function evaluation

Assessment report — exposure vs. maturity by function

VeloRisk gives CFOs, compliance officers, and internal audit leaders a living fraud risk program — run it on demand, not just once a year. Scenario-level analysis across asset misappropriation, financial statement fraud, corruption, and digital fraud, with findings mapped to FATF 40 and FTC Red Flags.

Audit-ready findings, not just checklists. A program your board and regulators will trust.

The Cost of an Unproven Program

The ACFE estimates organizations lose approximately 5% of revenue to fraud annually. Most incidents aren't caught by controls — they're discovered by accident, after the fact. A documented fraud risk program is what changes that equation.

Financial Exposure

No program means less visibility, not less fraud

Organizations without a structured fraud risk program don't have less fraud. They see less of it. Control gaps go undetected until an incident forces the conversation no one wanted to have.

Insurance & Audit

Fidelity and crime carriers are asking harder questions

Underwriters for fidelity, crime, and D&O coverage increasingly evaluate whether organizations have documented fraud risk programs. Auditors ask the same question. The answer is yes before they ask.

Board Accountability

When fraud surfaces, boards ask what was known

A fraud incident without a documented risk program leaves leadership exposed. A board-ready report showing known risks and documented controls changes the accountability conversation entirely.

How It Works

Self-paced Assessment

  • • Multiple-choice, self-paced, no preparation or scheduling
  • • Questions adapt to your organization and industry

The Candor™ Analysis Engine

  • • Fraud schemes identified and prioritized for your industry and context
  • • Control gaps ranked by what to fix first
  • • Findings mapped to FATF 40 and more

Comprehensive Reports + Platform

  • • Executive Report (~25 pages) for board, audit committee, and insurance presentations
  • • Practitioner Report with prioritized findings, control gap analysis, and remediation recommendations
  • • Interactive platform for ongoing access, KPI tracking, and remediation management

On-Demand Reassessment

  • • Re-run after a loss event, control change, or new fraud typology, pre-filled with your previous answers
  • • Compare results across runs with the Assessment Comparison section
  • • Unlimited reassessments included with the annual program

Built for Leaders Who Answer for the Fraud Program

VeloRisk's Fraud Program is built for CFOs, compliance officers, and internal audit leaders who run a fraud program they can prove works — not a one-time snapshot.

Common Use Cases

  • •
    Internal Audit Preparation: Documenting fraud risk program maturity ahead of audits
  • •
    Regulatory Examination Readiness: Demonstrating fraud control coverage to examiners
  • •
    Board Reporting: Presenting fraud risk posture and program gaps to the board or audit committee
  • •
    M&A Due Diligence: Evaluating fraud risk exposure in acquisition targets
  • •
    Insurance Applications: Supporting fidelity bond or crime insurance applications
  • •
    Program Gap Analysis: Identifying control weaknesses before they become incidents

Start Your Program.

No hidden fees. No surprises.

Discounted rate — save 40% off standard pricing. It's available for a limited time; standard pricing applies at renewal and to new purchases after this window closes.

Annual Program

Save 40%

$12,499/yr
$7,499 /yr
Tax included · Renews annually
  • Unlimited reassessments & re-runs for 12 months
  • Assessment Comparison report section (year-over-year)
  • Unlimited participants
  • Executive + Practitioner Reports (2 PDFs)
  • Interactive online platform
Start Your Diagnostic

Running multiple programs? See bundle pricing →

What to expect after purchase

1

Complete checkout

Takes about 2 minutes

2

Log in to your account

Access granted immediately

3

Start your assessment

No setup. Platform guides you through everything.

30-Day Satisfaction Guarantee

Not satisfied for any reason within 30 days? We'll refund 100% of your purchase — no back-and-forth. See full policy →

Mapped to the Frameworks That Matter

Findings Mapped to

  • FATF 40 Recommendations
  • FFIEC Authentication Guidance
  • FTC Red Flags Rule
  • GDPR
  • NIST CSF 2.0
  • NIST SP 800-53
  • NIST SP 800-63 (Digital Identity)
  • PCI DSS v4.0.1

Security & Privacy

  • Data encrypted at rest and in transit
  • No data sharing with third parties
  • You keep full ownership of your data and reports
  • Multiple-choice answers only: no free text or document uploads
  • Hosted on Google Cloud Platform (SOC 2 Type II certified infrastructure)

Frequently Asked Questions

How long does the assessment take?

Most users complete their initial diagnostic assessment in 2-3 hours, one time. The assessment is self-paced — you can pause and resume at any time. No data collection or preparation is required before you start; the platform guides you through everything it needs to know about your organization. Future re-runs open pre-filled with your previous answers, so updates take a fraction of that time.

What does the fraud risk analysis cover?

VeloRisk analyzes your organization across fraud risk dimensions covering asset misappropriation, financial statement fraud, corruption, and fraud scheme scenarios specific to your industry and operational profile. The assessment adapts to your industry classification, organization size, and operational context, because fraud risk profiles differ significantly between a financial institution, a healthcare organization, and a technology company. Findings include prioritized control gaps, exposure ratings, and remediation recommendations, all mapped to other applicable frameworks.

What makes this a program, not just an assessment?

Fraud is continuous. A point-in-time assessment tells you where you stood the day you ran it. VeloRisk re-evaluates when it matters — after a loss event, a control change, or when new fraud typologies emerge. Unlimited reassessments and an Assessment Comparison section track movement over time. Your fraud risk posture stays current.

Who should complete the assessment?

The assessment is built for the person responsible for the fraud risk program—typically the CFO, Chief Compliance Officer, VP of Internal Audit, or a senior member of the audit committee. Involve as many participants as needed — input from finance, operations, legal, and IT is welcome.

What does the report include?

The Fraud Program Assessment produces a single comprehensive report containing: fraud risk exposure summary, scheme-level findings with likelihood and impact ratings, control gap analysis, prioritized remediation recommendations, and compliance mappings to FATF 40, FTC Red Flags, PCI DSS, and GDPR. The report is structured for internal practitioners and for presenting to auditors or examiners.

Is my data secure?

Absolutely. All data is encrypted at rest and in transit, hosted on Google Cloud Platform, whose infrastructure is SOC 2 Type II certified. We never share your data with third parties. You retain full ownership of all assessment data and reports.

Do you offer volume discounts or enterprise pricing?

Yes. Contact us for custom enterprise packages.

Stop assuming your fraud program works. Prove it.

Start today. No preparation required. Audit-ready reporting from day one.

Have questions? Contact us and we'll help you get started.