AI Risk Program

Find the AI Risk Nobody Assessed, Before It Reaches a Customer.

A diagnostic on how your organization governs AI: where an agent could act without approval, where sensitive data could surface in an output, and whether you could show the risk was assessed. Findings map to NIST AI RMF. Re-run it whenever your AI footprint changes.

Complete your initial diagnostic assessment in 2-3 hours. Self-paced — pause and resume anytime. No preparation required.

Tailored to your industry, company size, and operating geography — not a generic checklist.

CSA AICM • EU AI Act • MITRE ATLAS • NIST AI RMF • NIST CSF 2.0 • OECD AI Principles • OWASP LLM Top 10

Built by practitioners

Built by enterprise risk, fraud, and security risk practitioners

Secure by design

No names. No free-text. Nothing sensitive.

No AI agents

Auditable analysis. No autonomous actions. No black-box results.

The Failure Mode Isn't a Bad Metric. It's a Bad Headline.

AI deployments carry three recurring exposures, whether anyone has written them down or not.

An agent takes an action nobody approved.

Autonomous or semi-autonomous agents get granted more access as they prove useful. Nobody maps that access against what the agent is actually authorized to do until something goes wrong and the question is "who approved this."

Sensitive data ends up somewhere it shouldn't.

A model trained, fine-tuned, or given retrieval access to customer, employee, or proprietary data can surface it in an output or pass it to a third-party vendor without anyone deciding that should be possible.

A decision surfaces that nobody can defend.

A biased, discriminatory, or noncompliant output reaches a customer or regulator before anyone catches it - and there's no documentation showing the risk was ever assessed, only that it existed.

These rarely show up on a dashboard until after they've happened. VeloRisk assesses the governance program that determines whether you catch them before they do - or find out about them the same way your board and your regulator do.

See Your Program in Action

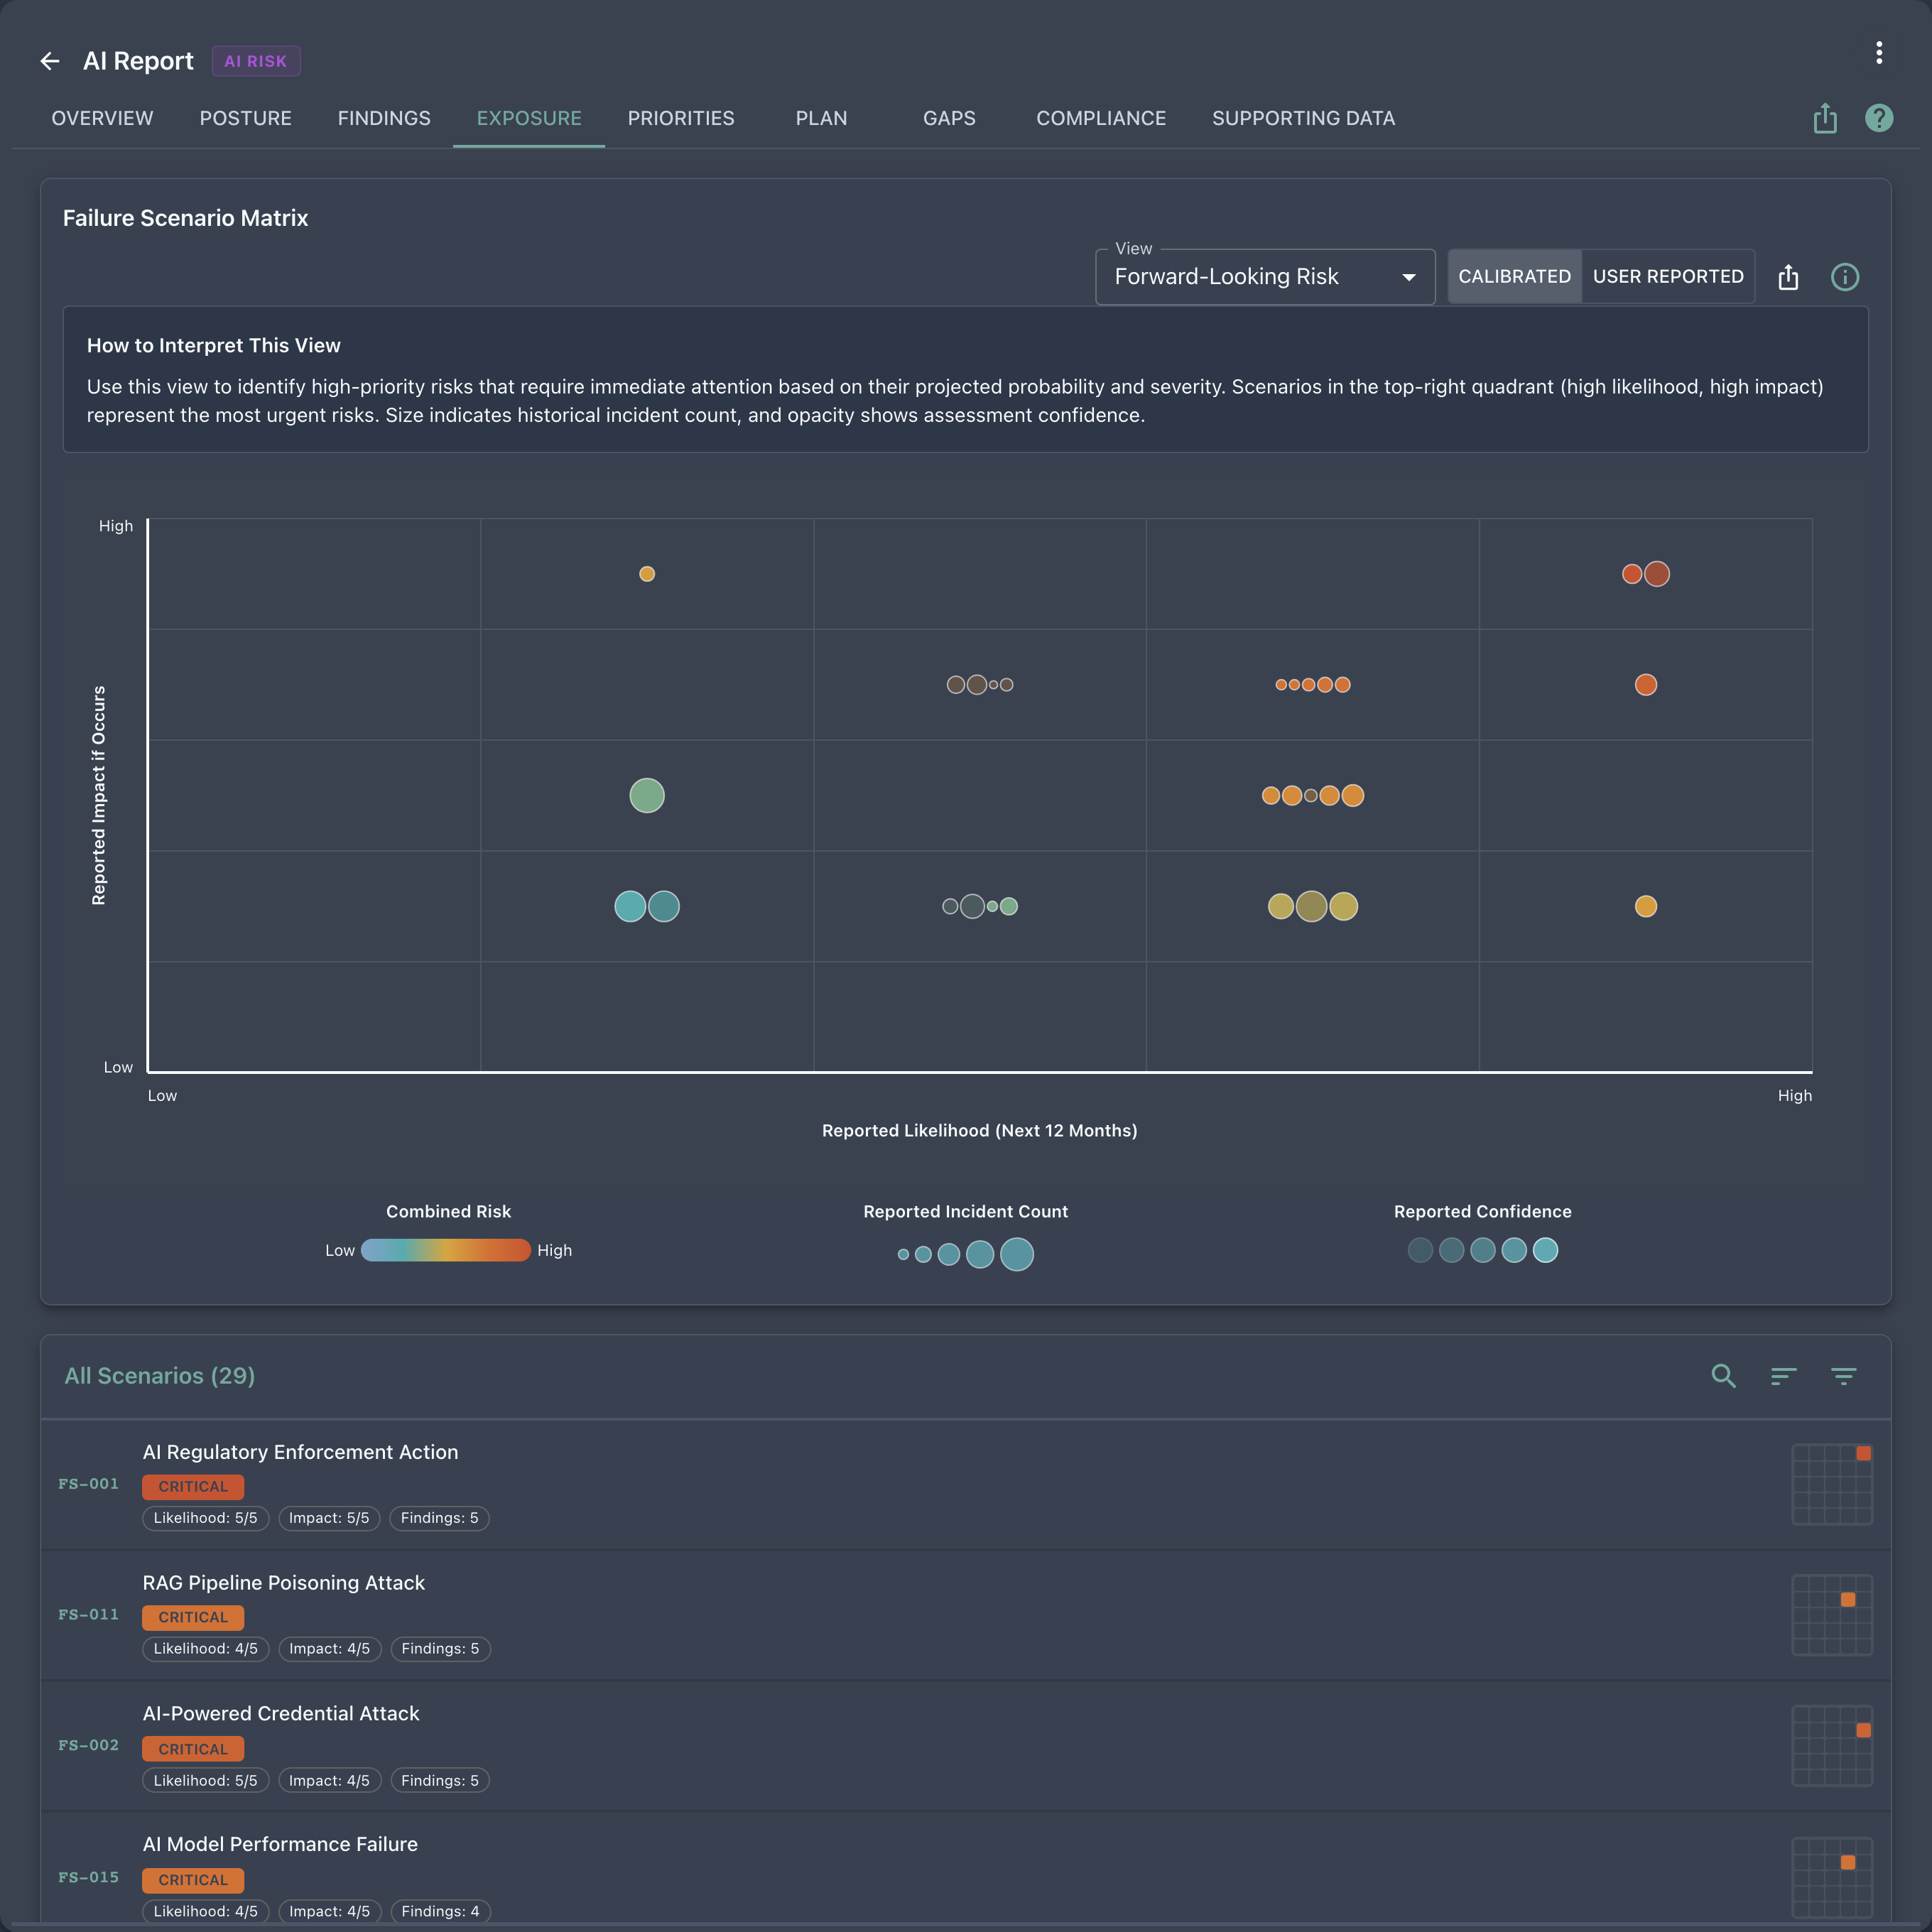
This is what the diagnostic hands you: findings by severity, failure scenarios by likelihood and impact, and what changed since your last run. Sample data.
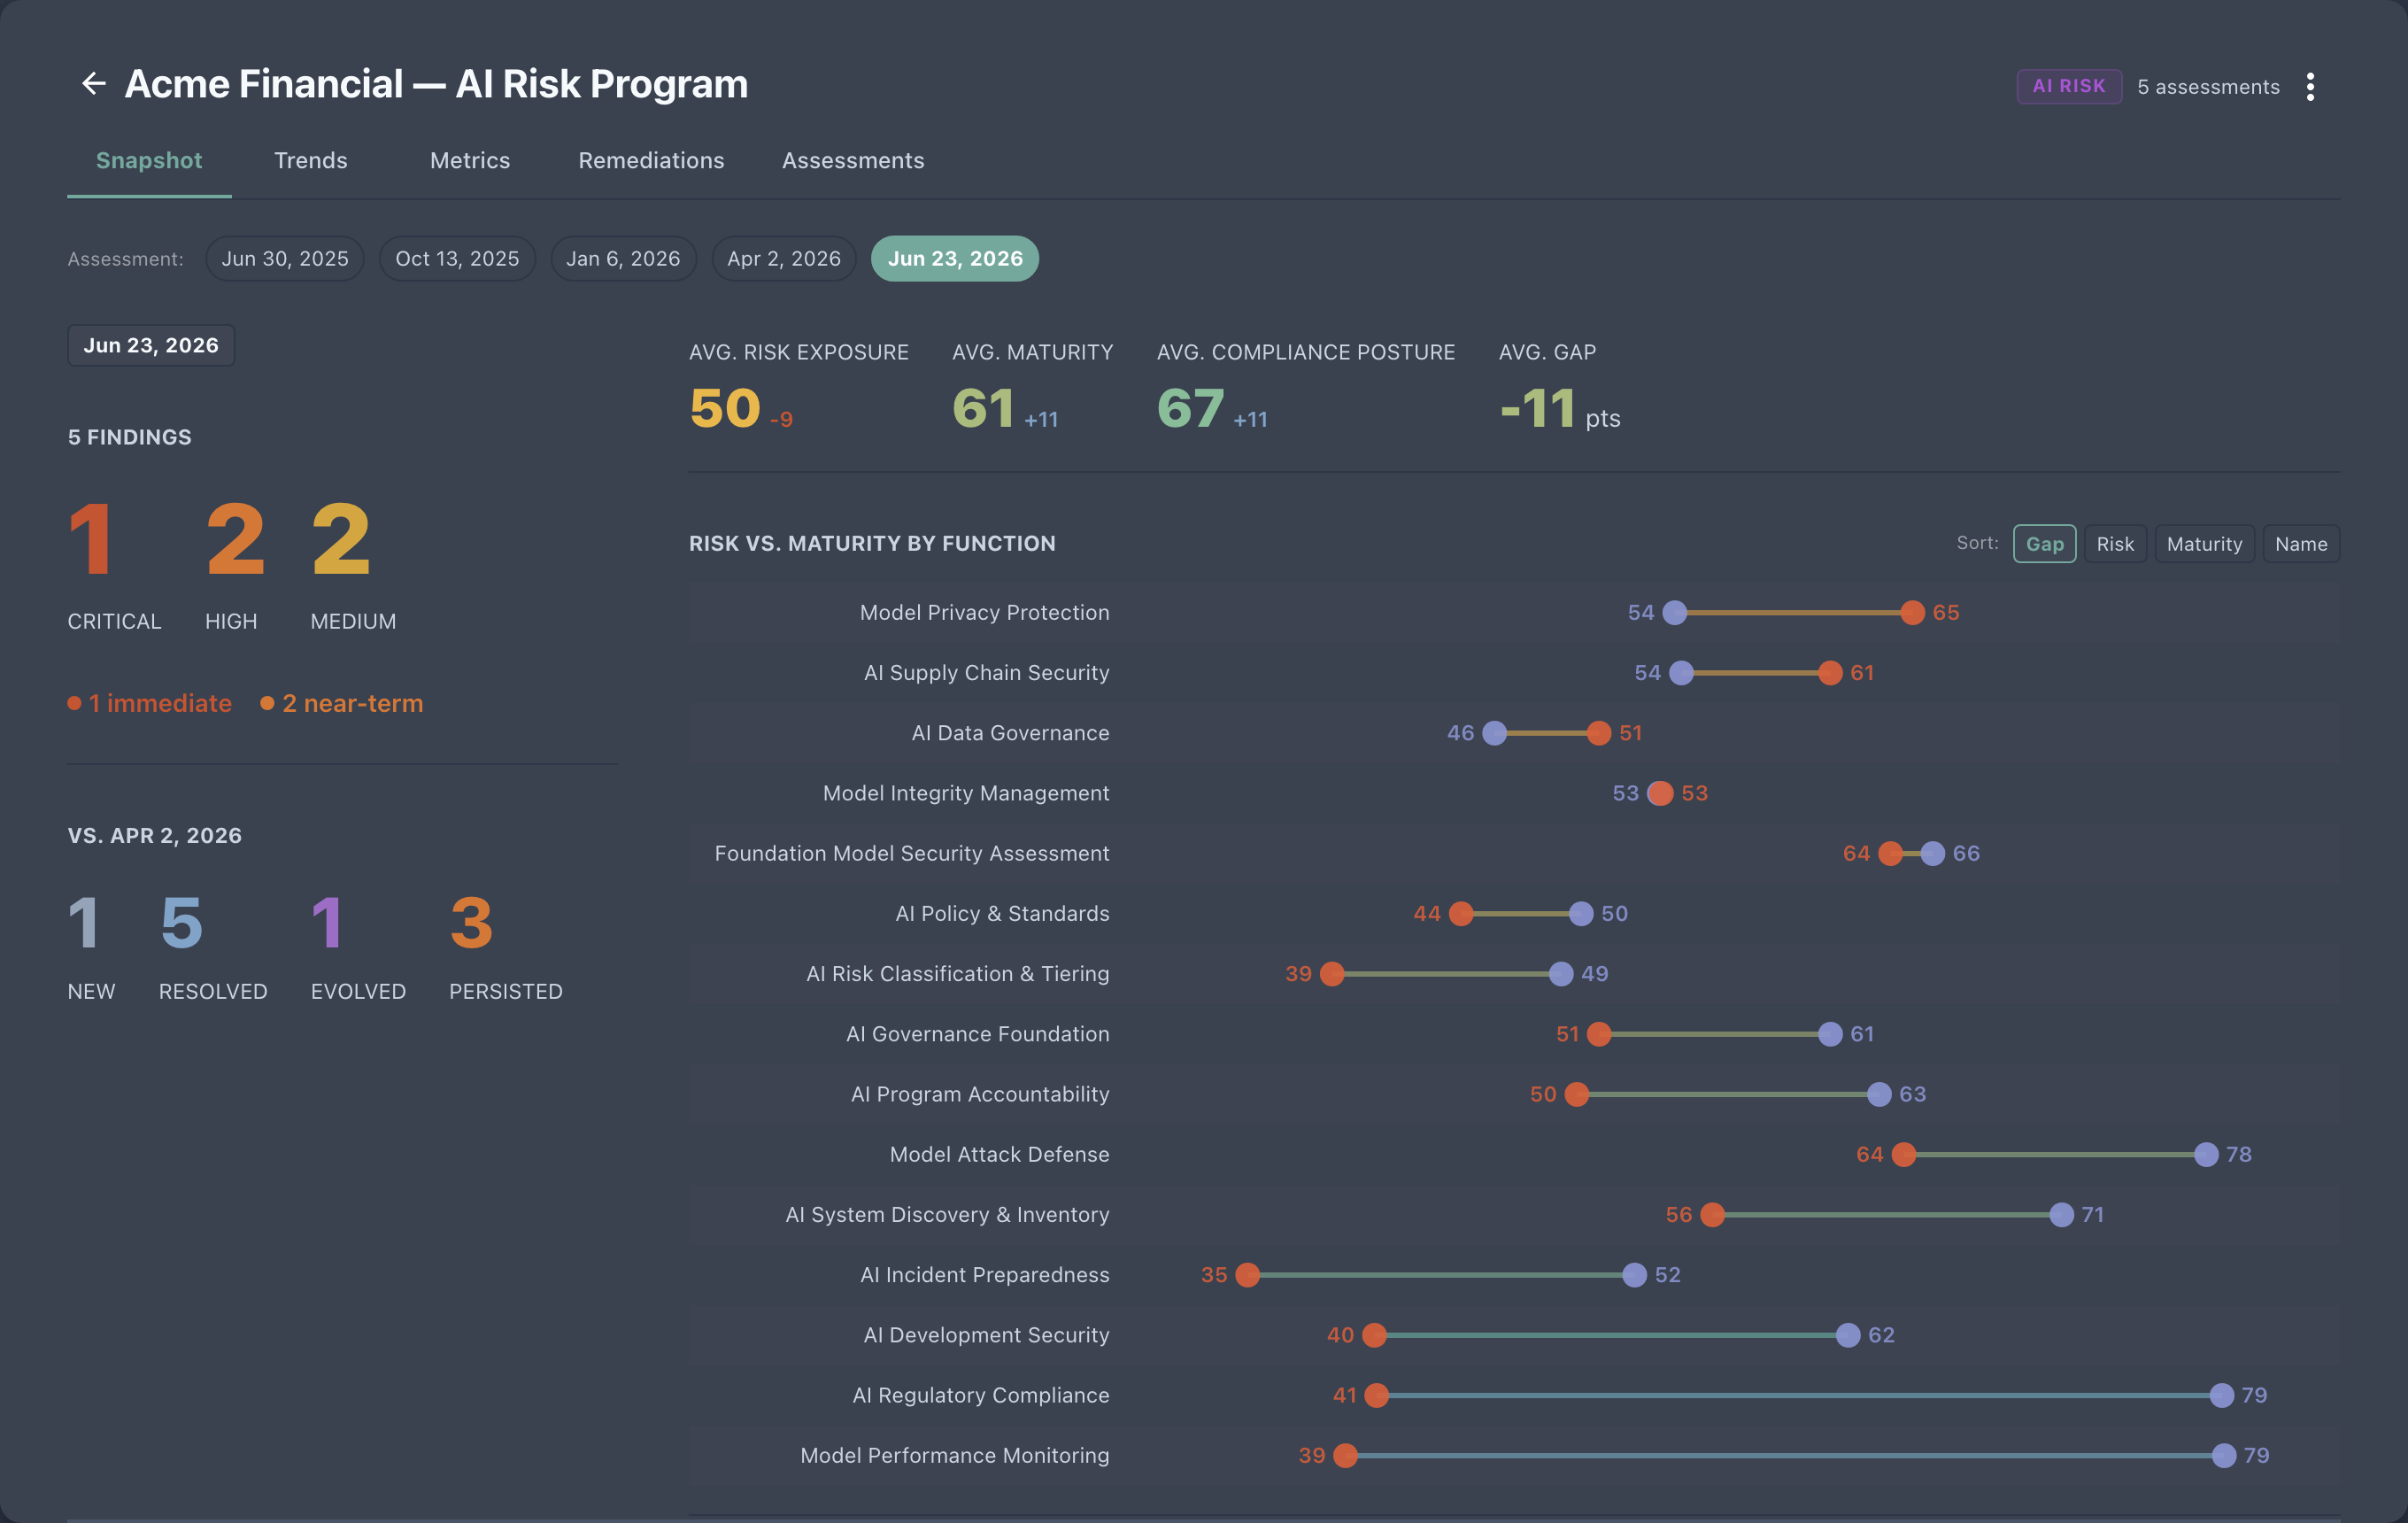
AI Risk Program Dashboard — AI/ML risk posture overview across domains

Program Dashboard — AI risk posture at a glance
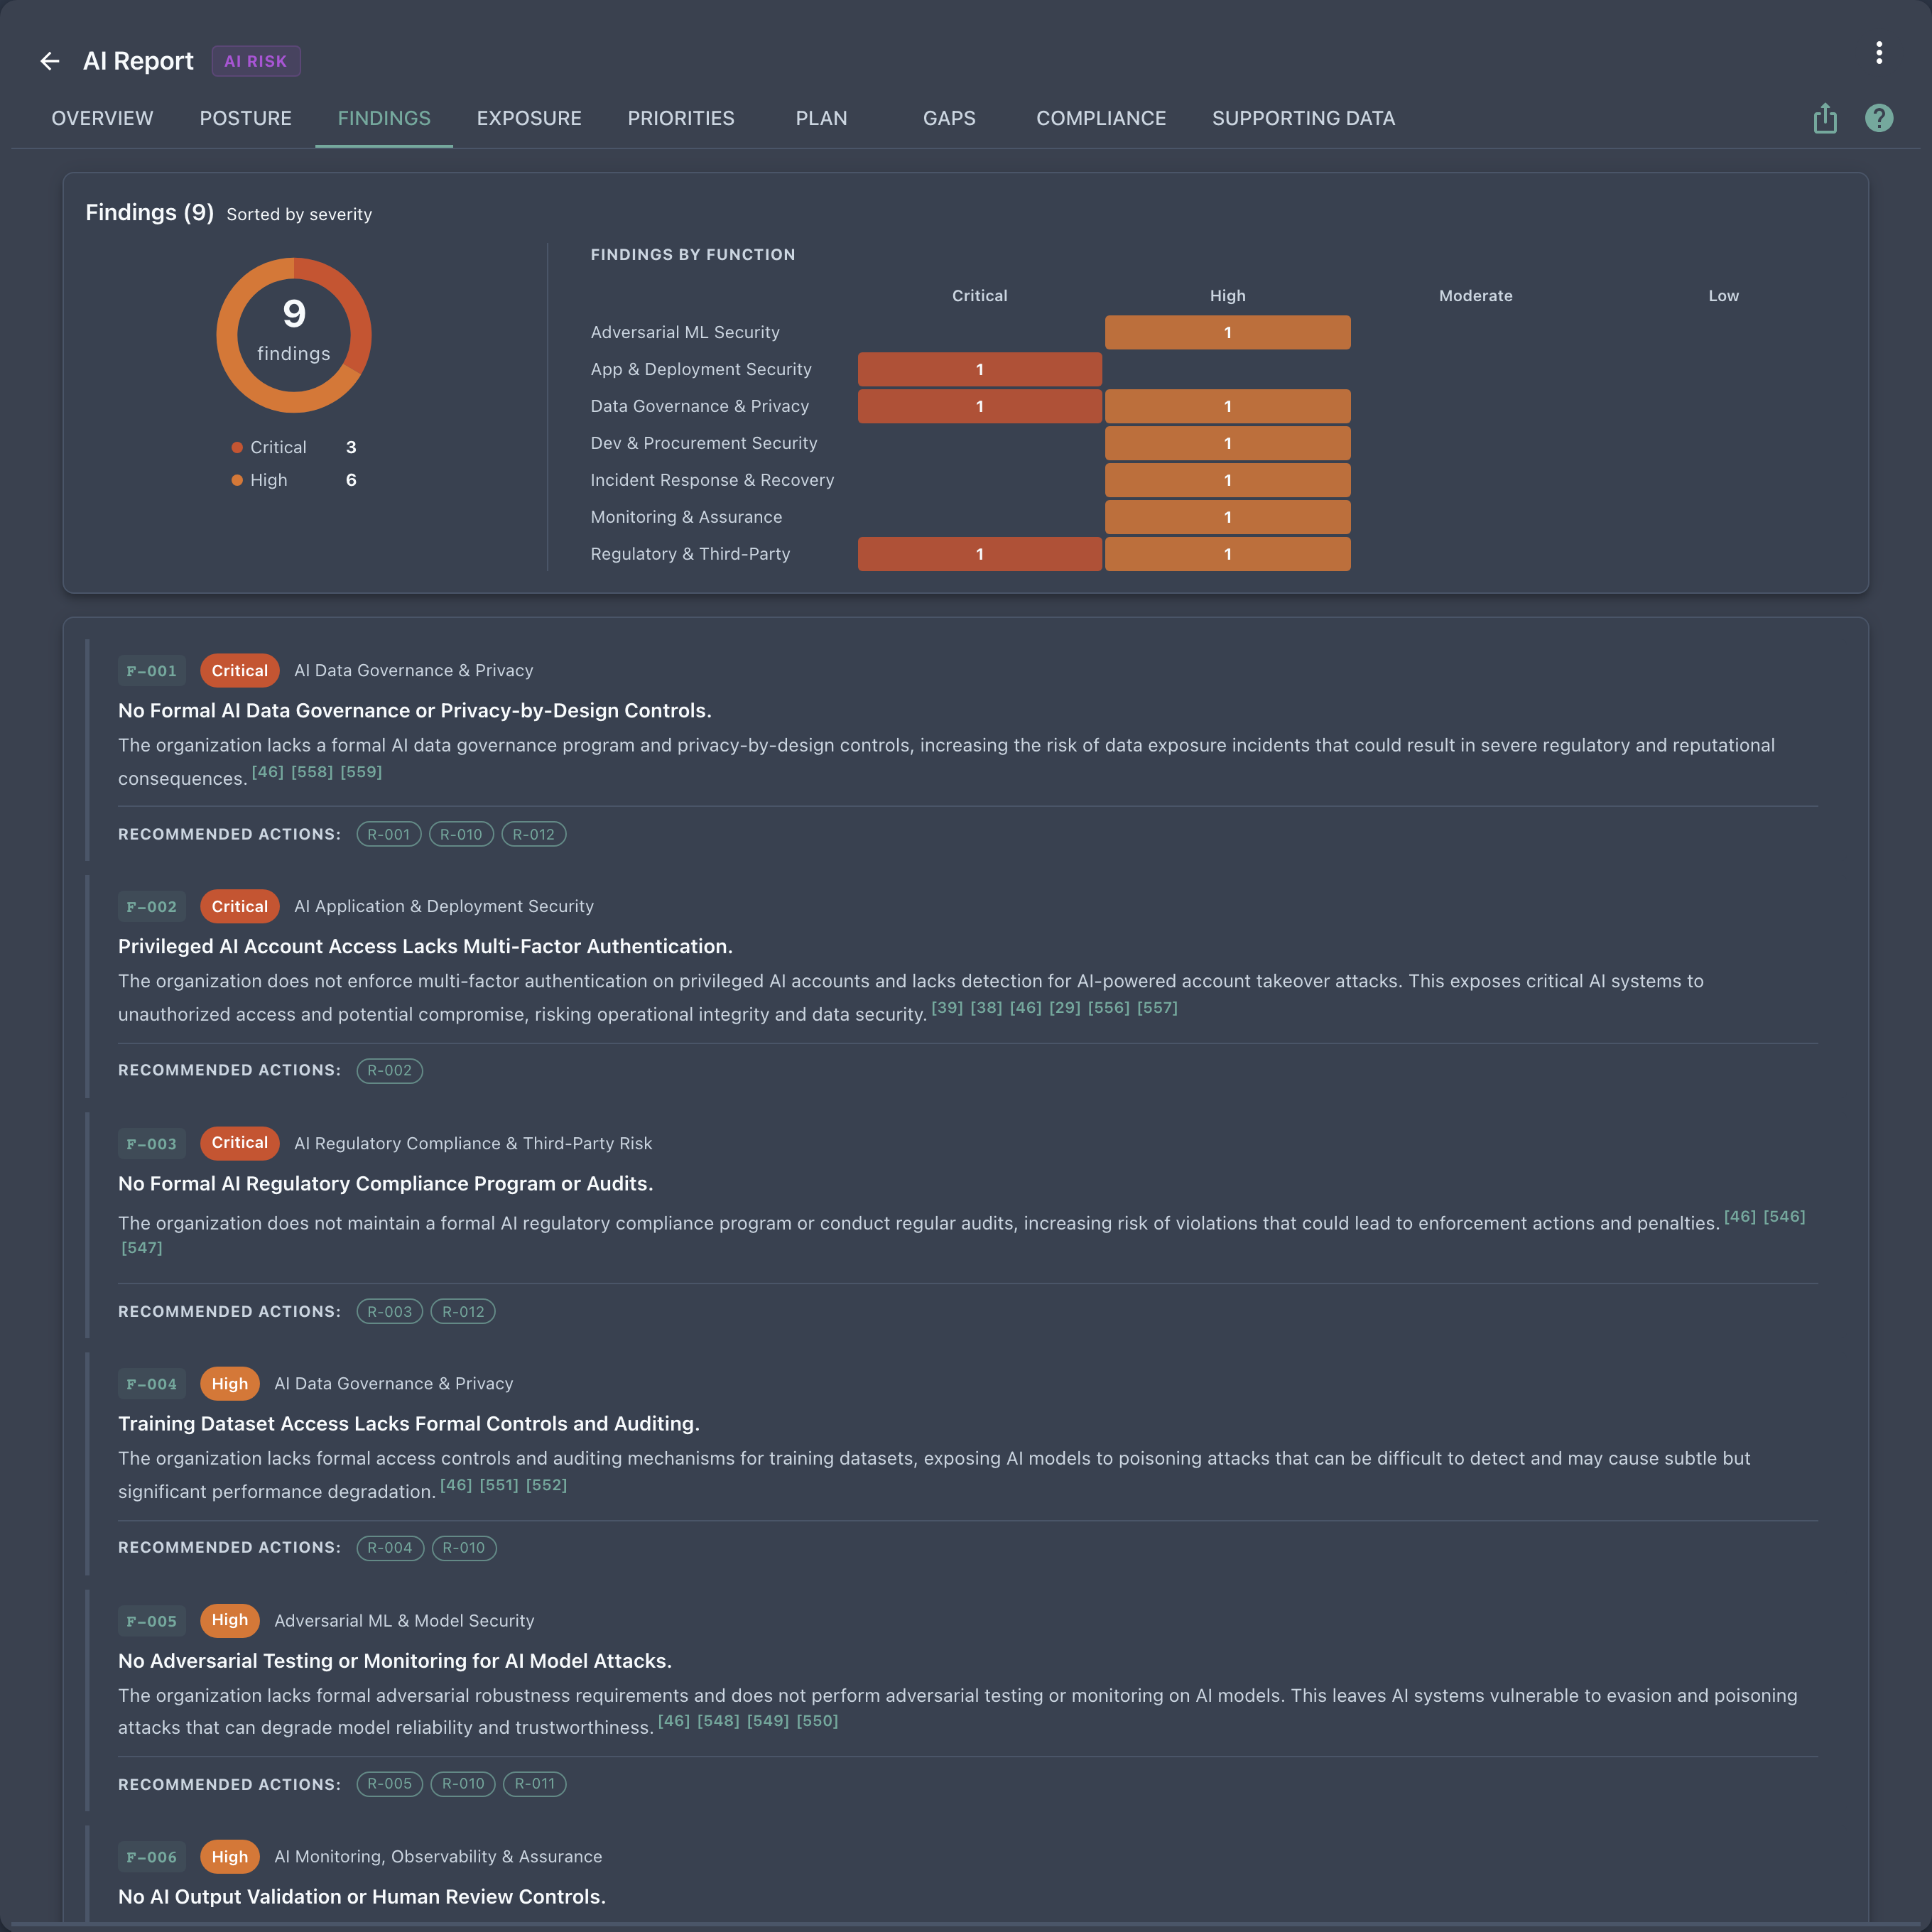
AI Risk assessment report — findings by severity and function with recommended actions
Assessment report — findings by severity and function

AI Risk assessment report — failure scenario matrix plotting risk likelihood against impact

Assessment report — failure scenarios by likelihood and impact

Start Your Diagnostic — from $7,499/yr

30-day satisfaction guarantee.

How It Works

Self-paced Assessment

  • • Multiple-choice, self-paced, no preparation or scheduling
  • • Questions adapt to how you use AI

The Candor™ Analysis Engine

  • • Governance gaps across the model lifecycle, data practices, and oversight
  • • Control gaps ranked by what to fix first
  • • Findings mapped to NIST AI RMF, MITRE ATLAS, and more

Comprehensive Report + Platform

  • • Separate executive and practitioner reports for board and technical audiences
  • • Prioritized findings with remediation recommendations
  • • Interactive platform for ongoing access to findings

On-Demand Reassessment

  • • Re-run when you deploy new models or expand AI use cases, pre-filled with your previous answers
  • • Compare results across runs
  • • Unlimited reassessments included with the annual program

Built for the People Accountable for AI

VeloRisk's AI Risk Program is built for CTOs, CISOs, Chief Risk Officers, and compliance leaders who need a living, board-ready program for their evolving AI governance posture.

Common Use Cases

  • •
    EU AI Act Readiness: Assessing exposure and governance gaps ahead of regulatory compliance deadlines
  • •
    AI Governance Program: Establishing or maturing your AI governance framework ahead of audits
  • •
    Board Reporting: Presenting AI risk posture and governance gaps to the board or audit committee
  • •
    Model Risk Management: Documenting AI model inventory, validation gaps, and oversight structures
  • •
    Vendor AI Risk: Evaluating third-party AI exposure across your supply chain
  • •
    M&A Due Diligence: Assessing AI governance maturity and regulatory exposure in acquisition targets

Start Your Program.

No hidden fees. No surprises.

Discounted rate — save 40% off standard pricing. It's available for a limited time; standard pricing applies at renewal and to new purchases after this window closes.

Annual Program

Save 40%

$12,499/yr
$7,499 /yr
Tax included · Renews annually
  • Unlimited reassessments & re-runs for 12 months
  • Assessment Comparison report section (year-over-year)
  • Unlimited participants
  • Executive + Practitioner Reports (2 PDFs)
  • Interactive online platform
Start Your Diagnostic

Running multiple programs? See bundle pricing →

What to expect after purchase

1

Complete checkout

Takes about 2 minutes

2

Log in to your account

Access granted immediately

3

Start your assessment

No setup. Platform guides you through everything.

30-Day Satisfaction Guarantee

Not satisfied for any reason within 30 days? We'll refund 100% of your purchase — no back-and-forth. See full policy →

The Governance Expectation Is Already Here

The EU AI Act is already in force, and its obligations phase in through 2027 and 2028. US federal guidance is accelerating. OCC model risk management requirements are already being applied to AI systems at regulated institutions. A documented AI governance posture is the baseline these regimes expect.

See what regulators expect ↓

EU AI Act — In Force, Phasing In

Governance obligations are phasing in. Documentation is the baseline.

The Act's prohibitions and core transparency duties already apply, and requirements for high-risk AI systems phase in through 2027 and 2028. Penalties for the most serious violations reach up to 7% of global revenue. The organizations that document governance now aren't scrambling when each date arrives. See the EU's official schedule.

US Regulatory Landscape

Multiple agencies, converging expectations

The CFPB, EEOC, OCC, and Federal Reserve have each issued AI-specific guidance with enforcement implications. OCC model risk management guidance (SR 11-7) is being applied to AI systems at regulated institutions right now.

Reasonable Steps, Documented

Regulators assess "reasonable steps" — you need to show them

A documented AI risk program — showing governance gaps identified, controls evaluated, and remediation prioritized — is the clearest evidence of reasonable steps before an examiner or plaintiff's attorney asks for it. Without it, you have no story to tell.

Mapped to the Frameworks That Matter

Findings Mapped to

  • CSA AI Controls Matrix (AICM)
  • EU AI Act
  • MITRE ATLAS
  • NIST AI Risk Management Framework (AI RMF 1.0)
  • NIST CSF 2.0
  • OECD AI Principles
  • OWASP LLM Top 10

Security & Privacy

  • Data encrypted at rest and in transit
  • No data sharing with third parties
  • You keep full ownership of your data and reports
  • Multiple-choice answers only: no free text or document uploads
  • Hosted on Google Cloud Platform (SOC 2 Type II certified infrastructure)

Frequently Asked Questions

How long does the assessment take?

Most users complete their initial diagnostic assessment in 2-3 hours, one time. The assessment is self-paced — you can pause and resume at any time. No data collection or preparation is required before you start; the platform guides you through what it needs to know about your AI footprint and governance environment. Future re-runs open pre-filled with your previous answers, so updates take a fraction of that time.

What makes this a program, not just an assessment?

Your AI footprint changes constantly — new models deployed, new use cases, new vendors. A one-time assessment is out of date the moment you ship the next model. VeloRisk lets you re-evaluate on demand when your AI posture changes. Unlimited reassessments are included with the annual program, so your governance documentation stays current as your AI program evolves.

Do we need to have a mature AI program to benefit from this assessment?

No. The assessment is valuable whether you're deploying AI extensively, just beginning to use AI tools, or primarily using AI through vendors and SaaS platforms. The assessment adapts to your current AI posture—organizations at any stage of AI maturity will get actionable findings.

Who should complete the assessment?

The assessment is for the person responsible for AI governance or technology risk—typically the CTO, CISO, Chief Risk Officer, Chief AI Officer, or a senior compliance leader. Involve as many participants as needed — legal, engineering, data science, and operations are all welcome contributors.

What does the assessment evaluate, and what does the report include?

VeloRisk analyzes your organization across AI governance dimensions including model inventory and lifecycle management, data governance practices, human oversight structures, third-party AI vendor risk, bias and fairness controls, explainability and transparency, and incident response readiness. The AI Risk Program Assessment produces two reports: an Executive Report for board and leadership audiences, and a Practitioner Report for technical and compliance teams. Both include an AI risk exposure summary, governance gap analysis by domain, prioritized remediation recommendations, and compliance mappings to EU AI Act, MITRE ATLAS, NIST AI RMF 1.0, NIST CSF 2.0, OECD AI Principles, OWASP LLM Top 10, and other applicable frameworks. Findings are prioritized by likelihood, impact, and remediation effort.

Is my data secure?

Absolutely. All data is encrypted at rest and in transit, hosted on Google Cloud Platform, whose infrastructure is SOC 2 Type II certified. We never share your data with third parties. You retain full ownership of all assessment data and reports.

Do you offer volume discounts or enterprise pricing?

Yes. Contact us for custom enterprise packages.

Your AI Risk Program, Running in Hours.

Start today. No preparation required. Board-ready AI governance from day one.

Have questions? Contact us and we'll help you get started.