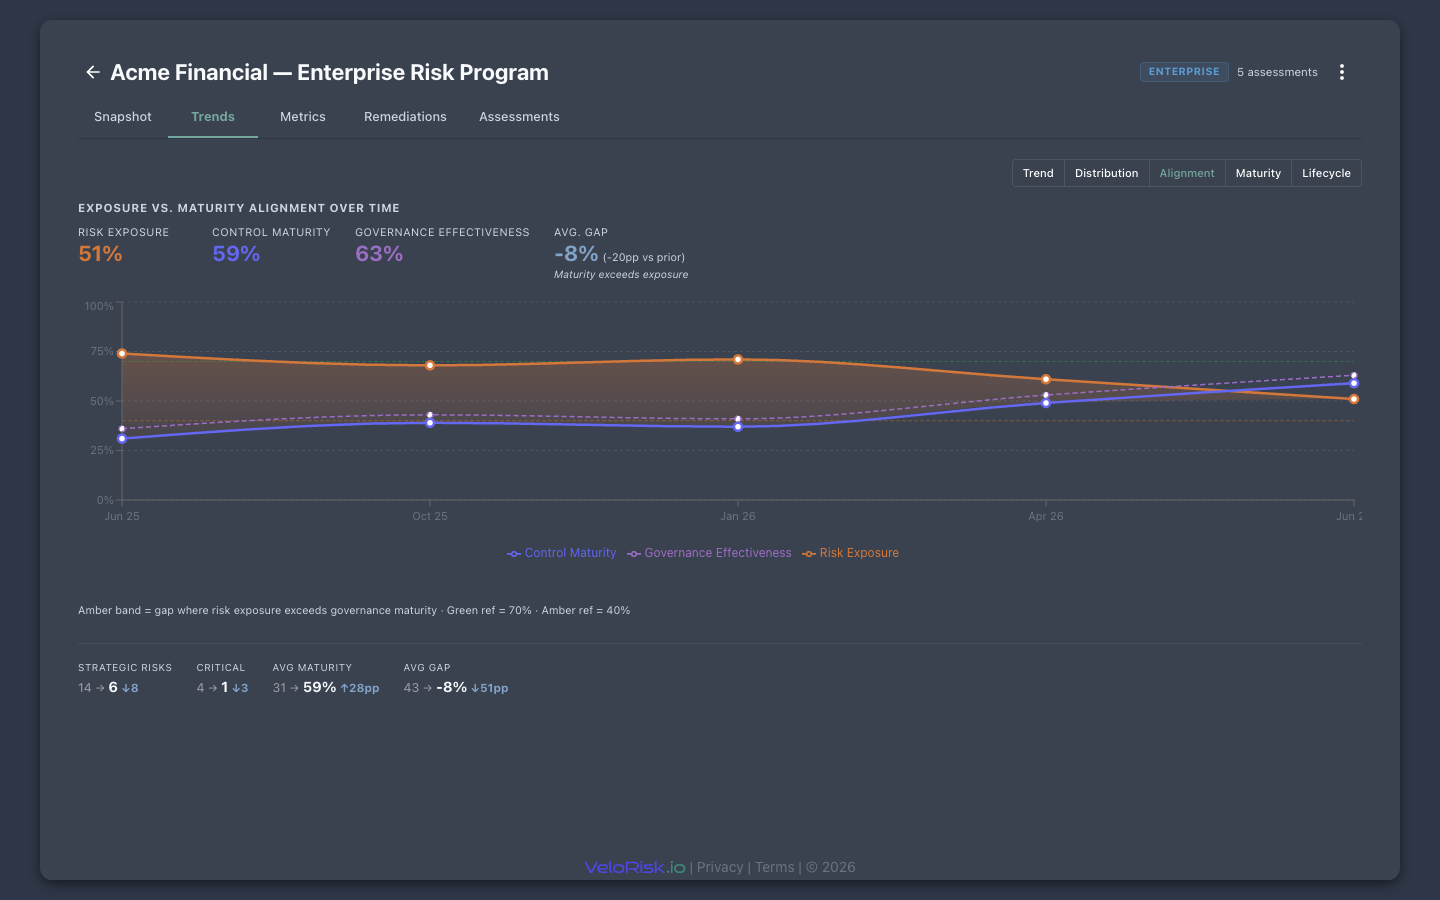
Knowing your risk exposure shouldn't take six months or six figures.

VeloRisk is the Risk Strategy Platform banks, credit unions, and fintechs use to run dynamic, responsive risk programs — AML/CFT, Fraud, AI, and Enterprise — always current, always examination-ready.

Start Your Risk Program

Built by practitioners

Fraud and financial crime professionals with 20+ years in detection, prevention, and risk program design.

Secure by design

No names. No open text inputs. Nothing sensitive.

No AI agents

Auditable, deterministic analysis. No autonomous actions. No black-box results.

Built for regulated financial institutions

Community banks, credit unions, fintechs, and MSBs face the same examination standards as the largest institutions — but without the same resources. VeloRisk was built to close that gap: board-ready risk programs that stay dynamic and responsive as your risk environment changes, not a static report that goes stale.

Exam coming up

Get a credible program in place before examiners arrive — not after.

New to the role

Know what you inherited before the examiner tells you what they found.

Peer got hit with enforcement

If a similar institution just received a consent order, your board is already asking questions.

How It Works

A Risk Strategy Program isn't a deliverable. It's something you run.

1

Launch Your Program

Complete your first assessment. Multiple-choice, 2-3 hours. Candor™, VeloRisk's analysis engine, evaluates your responses across thousands of risk dimensions and produces board-ready reports, prioritized findings, and compliance framework mapping — specific to your institution.

2

Act on Your Findings

Findings and remediations are living items in the platform — tracked and updated as your program progresses. Everything lives in your program, not locked in a PDF.

3

Re-run It When Things Change

Follow-up assessments update findings in place — new issues surface, resolved ones close out, evolved ones carry their history. Re-run before exams, after leadership changes, or whenever your risk environment shifts. Included at no extra cost.

Risk Strategy Programs

Each program gives you a current picture of your risk posture — and the platform to keep it current.

AML/CFT Program

For BSA Officers and Chief Compliance Officers at regulated financial institutions

  • BSA/AML program assessment & gap analysis
  • Regulatory examination preparation (OCC, FinCEN, FDIC)
  • FATF guidance alignment
  • Board reporting on AML/CFT risk

Scored against

COSO ERM FATF 40 FFIEC Auth Guidance FFIEC BSA/AML +8 more →
See This Program → Explore AML Program Governance for free →

Fraud Program

For fraud and risk leaders at fintechs and financial institutions

  • Internal audit preparation & fraud program maturity
  • Regulatory examination readiness
  • M&A due diligence
  • Board reporting on fraud risk

Scored against

ACFE FATF 40 FFIEC BSA/AML FTC Red Flags +9 more →
See This Program → Explore Regulatory Compliance & Fraud Response for free →

Enterprise Risk Program

For CISOs, CTOs, CFOs, and CROs at mid-market organizations

  • Enterprise-wide risk coverage across your full operating environment
  • Board reporting & governance
  • Due diligence for M&A, investment, or partnerships
  • Cyber insurance applications

Scored against

COSO ERM ISO 27001:2022 NIST CSF 2.0 SOC 2 +10 more →
See This Program → Explore Identity, Access & Security Resilience for free →

AI Risk Program

For CTOs, VPs of AI, and General Counsel at AI-forward organizations

  • EU AI Act readiness & governance gap analysis
  • AI governance program assessment & maturity
  • Model risk management & oversight documentation
  • Board reporting on AI risk

Scored against

EU AI Act NIST AI RMF 1.0 ISO/IEC 42001:2023 OWASP LLM Top 10 +4 more →
See This Program → Explore AI Inventory & Risk Classification for free →

CMMC Level 2 Readiness Assessment

Defense Contractors

For DIB contractors, DFARS-obligated organizations, and primes assessing supply chain compliance

  • SPRS score calculation across all 110 NIST 800-171 practices
  • Practice gap analysis with current-state documentation
  • Prioritized POA&M with SPRS score recovery projections
  • Pre-assessment readiness before your C3PAO engagement

Assessment Standard

CMMC 2.0 NIST SP 800-171 Rev 2 DFARS 252.204-7012
See This Assessment →

Not sure where to start?

Each program is built for a specific type of organization. Most start with one and add others as they identify gaps.

Program Organizations Typical buyer
Enterprise Risk Mid-market and enterprise organizations across industries seeking enterprise-wide risk coverage CISO, CTO, CFO, CRO
AML/CFT Regulated financial institutions — banks, credit unions, fintechs, MSBs, and payment companies with BSA/AML obligations BSA Officer, CCO, CRO
Fraud Fintechs, financial institutions, and any organization with material fraud exposure seeking a documented program Chief Fraud Officer, CCO, CFO, VP Risk, Internal Audit
AI Risk Organizations deploying AI in products, operations, or customer-facing systems with governance or regulatory exposure CTO, CISO, General Counsel, Chief AI Officer
CMMC Readiness Defense Industrial Base contractors and subcontractors with DFARS obligations preparing for C3PAO assessment IT Director, CISO, Contracts Manager
Need more than one program? Purchase a bundle — choose which programs to run on the platform after purchase.

Still unsure? Contact us — we'll help you figure out the right fit.

One Price. Every Reassessment Included.

Reassess as often as your risk environment changes, all year, at no extra cost. Starting at $7,499/yr — save 40%, for a limited time.

See Full Pricing

30-day satisfaction guarantee, no back-and-forth.

Your risk environment is changing. Your program should keep up.

Choose your program and get started today. No preparation required.

Start Your Risk Program

Not sure which program you need? Contact us and we'll help you find the right fit.